RACGP accreditation:the IT evidence.
We help you prepare and maintain the IT records for RACGP accreditation, and we’re available on survey day to answer IT questions. Below is a practical checklist, with references to the 5th and 6th editions so you can find the relevant guidance.
Where the 6th edition stands · checked 4 November 2026
The RACGP published the Standards for general practices, 6th edition, on 26 August 2026. Accreditation still uses the 5th edition for now. The Australian Commission on Safety and Quality in Health Care will publish how the move works. Your accrediting agency will tell you how your next assessment works. Once the transition period ends, every practice is assessed against the 6th edition. Until then the Commission encourages practices to start putting the 6th edition in place. We update this page when the dates are published.
What F8 covers, summarised. This is our summary. The RACGP's own wording is on racgp.org.au.
- F8.A
A plan for keeping systems running and recovering them: backups, protection against malware and intrusion, and what you do in a cyber incident, including telling patients when their data is involved. (5th edition: C6.4D.)
- F8.B
A named person responsible for information security, and written rules for where information is stored and who can access it. (5th edition: C6.4A and C6.4B.)
- F8.C
Digital communication with patients that protects their privacy. (5th edition: C6.4F.)
- F8.D
Social media use that protects patients and staff. (5th edition: C6.4G.)
- F8.E
How records are stored, how long they are kept and how they are destroyed, digital and paper. (5th edition: C6.4E.)
- F8.F
Telling patients which digital tools the practice uses in their care. This part is aspirational and is new in the 6th edition.
One piece of C6.4 moved elsewhere: who may access clinical information and official documents (C6.4C) is now F9.B, under privacy and confidentiality.
What the surveyor asks for
A named person responsible for ICT, and a written agreement.
Comes from: your IT support agreement, or a one-page note if you look after IT yourselves.
The backup log, and a restore test.
The log shows the jobs ran and what was done about failures. A record of a restore test helps show whether the backup can be used to recover the practice’s data. Comes from: whoever runs the backup. If they cannot produce both, the practice has a gap to fix before the survey.
A patching report.
It shows which machines got which updates, and when. Comes from: the monitoring software, or the person who clicks Update.
The user list, and when it was last reviewed.
It covers the clinical software, Windows, email, remote access and My Health Record. Comes from: a review on a schedule, and a procedure for the day someone leaves.
Written policies that describe your practice.
The privacy policy has to say how health information is stored and who can access it, including remotely. There must also be written rules for email and other digital communication, social media, and keeping and destroying records. The My Health Records Rules require a My Health Record security and access policy as well. Comes from: your policy manual. See policies below.
A cyber incident response plan that has been tested.
F8 expects it to be tested regularly. Comes from: a written plan, and a short walk-through of a made-up incident with the people named in the plan. We suggest at least once a year.
Business continuity for ICT.
It says what happens if the server dies or the internet is cut, and how long until the clinical software is back. Comes from: recovery targets agreed with your provider.
Disposal records.
These are certificates or a register showing drives were wiped or destroyed before equipment left. Comes from: whoever took the old computers away.
Staff security training records.
They show who was trained and when, and the results of any phishing tests. Anyone who uses My Health Record must be trained before they get access and every year after. Comes from: the training provider, or a log you keep.
Common gaps in accreditation evidence. The Commission publishes how many practices had to fix each indicator before they were accredited. From April 2023 to September 2026, under the 5th edition, the business continuity and information recovery plan (C6.4D, now part of F8.A) was the eighth most common of 125 indicators. 790 practices had to fix it before they were accredited. It asks for a backup log, current antivirus and firewalls, backups kept away from the practice and a recovery plan that has been tested: items 2 and 7 above. How records are stored, kept and destroyed (C6.4E, now F8.E) was 23rd, with 513 practices.
The long version, with what to fix first, is our guide: RACGP 6th edition, Criterion F8: the IT evidence to have ready.
How we keep the file current
Almost everything on the list above is produced by ordinary, well-run IT. For the practices we look after, the evidence comes out of the work and is filed as it happens:
- Our support portal tracks ten measures, from backups and restore tests to patching, staff access and security software. The practice manager sees the status of each and, for those in place, when we last verified it.
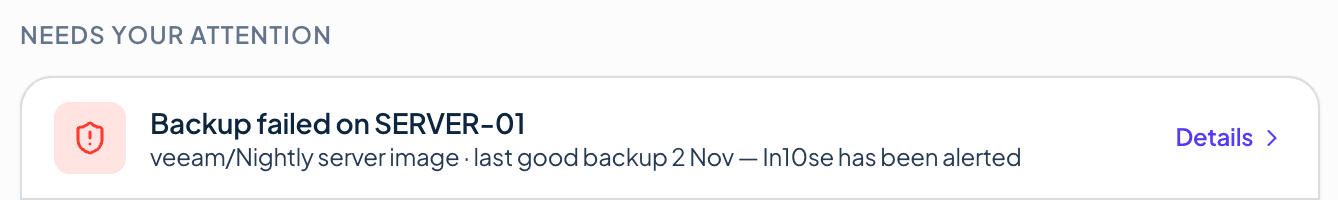
- We read the backup results every morning. A failed job raises a ticket the same day and shows on the practice's portal home page.
- Once a year, we test both the full server backup and the separate database backup. This is part of backup and recovery ($16.50 a workstation and $99 a server a month).
- We patch out of hours, and the portal shows the date we last verified it.
- We review access and remove leavers, and the portal shows the date of each check.
- We give you the wipe and recycling certificates for the equipment we retire.
- We write an incident response plan with the practice manager. Then we walk the people named in it through a made-up incident, so they know who calls whom.
- We prepare the IT Compliance Summary for the surveyor on request, and one of us can be on site on survey day if you want.

All of this is included with IT support, so accreditation IT support needs an IT support agreement with us. More on IT support. The rest of the portal, from tickets to the service report, is on how support works.
Policies
F8 names some policies and the My Health Records Rules require another. Each one has to describe what your own practice does, so we write them with the practice manager. This is part of accreditation IT support, which is included with IT support:
- Access and passwords, including multi-factor authentication
- Remote access and working from home
- Mobile devices and USB storage
- My Health Record security and access, written to the My Health Records Rules 2026
- A cyber incident response plan, walked through with the people in it
- Privacy and data breach response, consistent with the Privacy Act, the Australian Privacy Principles, the Notifiable Data Breaches scheme and the Health Records Act (Vic)
These are written for the practices we look after. They are not downloadable from this site.
If your My Health Record policy is more than a few months old, check it. The My Health Records Rules 2026 replaced the 2016 Rule. Since 1 October 2026 the security and access policy has to meet the new rules. They ask for training before access and every year, and a review at least once a year. Each version needs a number and a date. Records of user accounts and training are kept for five years. A policy written to rule 42 of the old Rule is out of date. The OAIC publishes guidance and a template.
The policy and procedure manual itself is a separate job. F8 and every other criterion point back to it. Our app Heathwren takes an existing 5th-edition manual and works out where each piece belongs under the 6th edition. It moves the content without changing a word and gives you a report of what moved where to check. Reading and searching the manual stay free for as long as the clinic wants. The move costs from $770, which includes the first year of editing. After that, editing is $790 a year.
Questions
Do we need to do anything about the 6th edition now?
Accreditation still uses the 5th edition, and the Commission encourages practices to start implementing the 6th now. Read it and check your manual against it. Your accrediting agency will tell you when your assessments move over. Check the requirements for your assessment with your accrediting agency.
Is the IT evidence different under F8?
Mostly the headings moved. A named person for IT security, backups and recovery, email and other digital communication, social media, and how records are kept and destroyed were all in C6.4 and are all in F8. Unique logins to the clinical software moved to F9.B, under privacy. The new part is F8.F, telling patients which digital tools the practice uses, and it is aspirational.
Will you be there on survey day?
Yes, if you want us there, to answer the IT questions directly.
What does an accreditation review cost?
Nothing extra. Accreditation IT support is part of our IT support, so it needs an IT support agreement with us.
Ask about accreditation IT support.
Tell us about your upcoming assessment and the IT records you already have. We’ll discuss how we can help and what to review next.